CEB Contributor
Michelle Guadalupe Treviño
Privacy, AI and Technology Attorney at Independent Privacy, AI & Technology Counsel
Michelle Guadalupe Treviño is a California attorney whose practice focuses on privacy, artificial intelligence governance, data protection, and technology transactions. She has worked with Shipt, Sephora, Meta, and Google (work for Meta and Google performed through outside legal and consulting engagements), advising leading global technology companies, multinational enterprises, and emerging growth companies on complex privacy, AI, and technology matters. These matters include privacy-by-design, AI governance, regulatory compliance, policy development, product counseling, commercial transactions, and cross-functional risk management. Her experience spans privacy compliance, intellectual property litigation, technology transactions, and strategic legal counseling, enabling her to advise organizations on navigating complex legal, regulatory, and business challenges in an evolving technology landscape.
Ms. Treviño earned her J.D. from the University of San Francisco School of Law and her BA from the University of California, Berkeley.
Ms. Treviño has completed the Chief Privacy Officer Program at UC Berkeley Law Executive Education in June of 2026 and holds the IAPP’s Fellow of Information Privacy (FIP) designation, along with the CIPP/US, CIPP/E, CIPP/C, CIPM, and AIGP certifications.
CEB Region:
Bay Area RegionPractice Areas:
Intellectual Property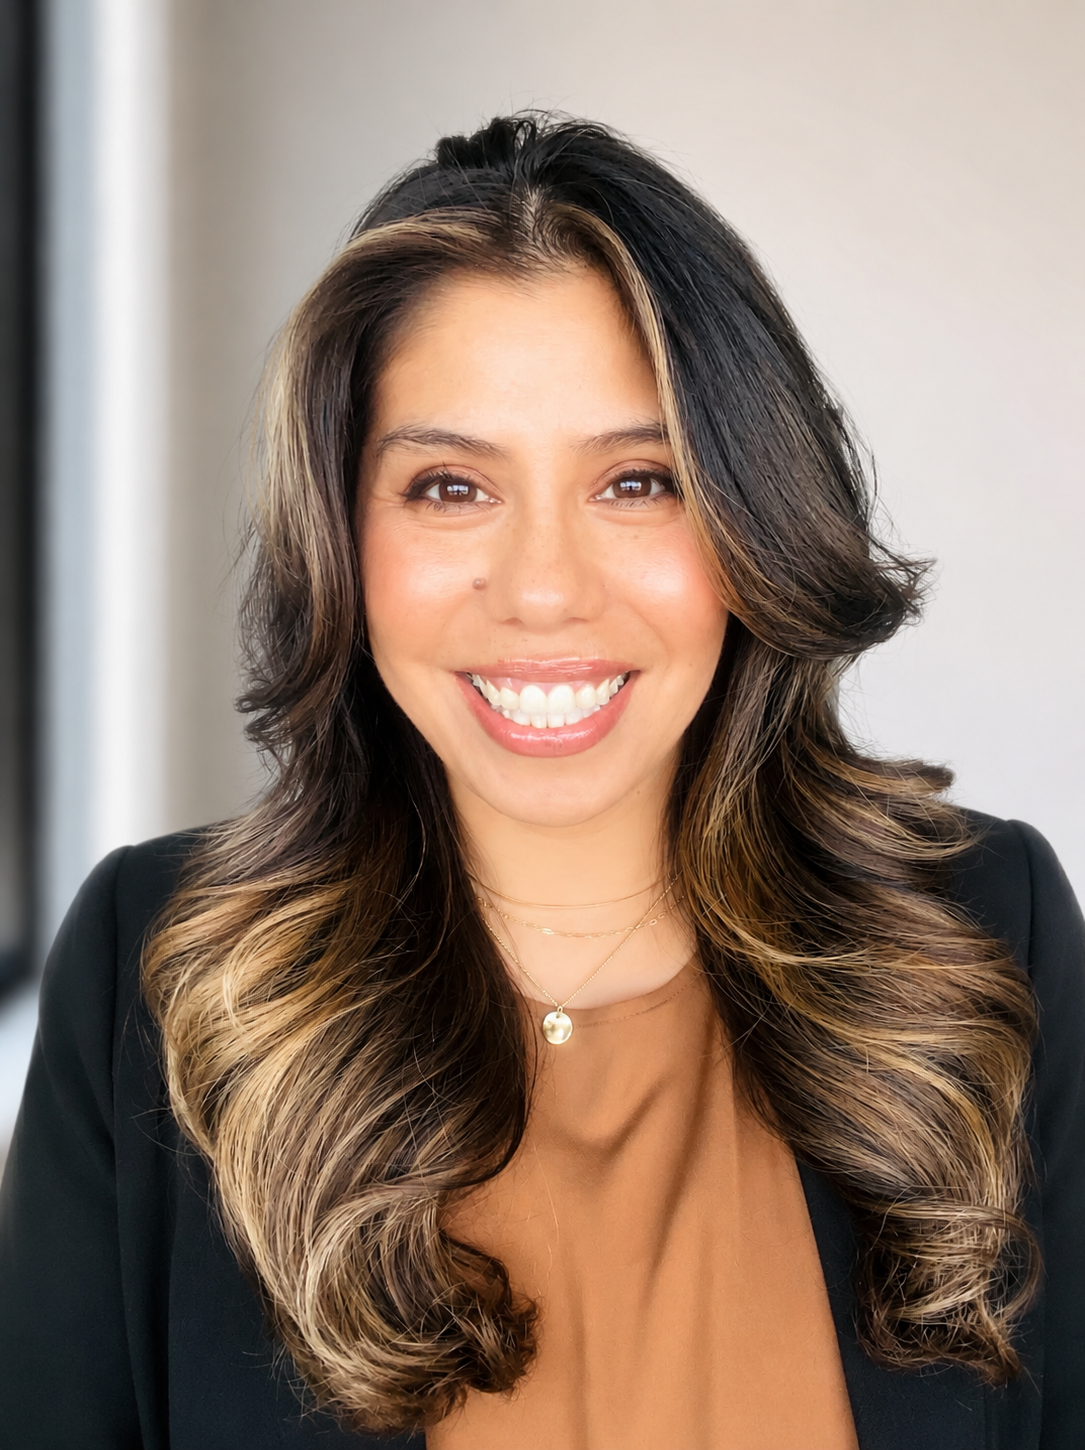
Content by Michelle Guadalupe Treviño
No articles found.
-
California Privacy Risk Assessment Checklist
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy
In-house counsel and relevant business stakeholders may use the following checklist to confirm that the required privacy risk assessment steps have been completed, documented, and approved. We completed legal editing and analysis of authorities cited here as of the date listed below.
-
Checklist - Do Not Sell or Share and GPC & Opt-Out Implementation
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy
Use the following checklist to identify key considerations when evaluating the sale or sharing of personal information under California's Consumer Privacy Act (CCPA), as amended by the California Privacy Rights Act (CPRA) (Civ. Code, §§ 1798.100–1798.199.100). The checklist helps in-house counsel identify activities that may constitute a sale or sharing of personal information under the CCPA, evaluate applicable compliance obligations, and determine necessary actions or further legal review.
-
Navigating Do Not Sell or Share and GPC & Opt-Out Requirements (Privacy)
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy
Determine whether activities constitute the sale or sharing of personal information under California law, identify associated privacy risks and compliance obligations, and determine appropriate next steps. We completed legal editing and analysis of authorities cited here as of the date listed below.
-
Conduct a California Privacy Risk Assessment
Privacy & Information Security, Information Security Planning, Handling Internet and Electronic Data
This how-to guide provides in-house counsel with a framework for determining when a California risk assessment is required and for conducting the assessment. We completed legal editing and analysis of authorities cited here as of the date listed below.
-
Sample Executive Summary Evaluating Tracking-Technology Exposure
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy
This sample executive summary addresses tracking technology exposure to digital properties subject to California law, including potential legal and regulatory exposure. We completed legal editing and analysis of authorities cited here as of the date listed below.
-
Sample Data Processing Addendum
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
The following Standard Document is an example of a Data Processing Addendum. The following should be used only as a general guide and not as a “fill in the blank” document.
-
Comparing California’s Privacy Framework to Other State Comprehensive Privacy Laws
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Compare the California Consumer Privacy Act of 2018 (CCPA), as amended by the California Privacy Rights Act of 2020 (CPRA) (Civ. Code, §§ 1798.100–1798.199.100), with other comprehensive state privacy laws. We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Using the CCPA as a Framework for Multi-State Privacy Compliance
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Provide your client with a strategic, practical framework for applying the California Consumer Privacy Act of 2018 (CCPA) (Civ. Code, §§ 1798.100–1798.199.100), as amended by the California Privacy Rights Act of 2020 (CPRA). We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Checklist: Steps for California Businesses to Meet Obligation to Protect Personal Customer Information
Privacy & Information Security, Types of Privacy Protections, Financial Data Privacy, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Review the steps a California business should take to meet its obligation to protect personal information as required by California privacy and data security laws. We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Sample Data Processing Agreement
Privacy & Information Security, Types of Privacy Protections, Information Security Planning
The following Standard Document is an example of a Data Processing Agreement (DPA). The following should be used only as a general guide and not as a “fill in the blank” document.
-
Navigating Internet and Computer Privacy Protections for Businesses And Others
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Determine whether activities constitute the sale or sharing of personal information under California law, identify associated privacy risks and compliance obligations, and determine appropriate next steps. We completed legal editing and analysis of authorities cited here as of the date listed below.
-
Checklist: Electronic Agreements for Websites Offering Goods and Services Online to Consumers
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Use this checklist to review or draft electronic agreements on a consumer-facing website offering goods and services online to consumers that comply with applicable privacy laws and regulations. We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Obtain Pre-Dispute Consent to Jurisdiction Over Internet Transactions
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Obtain pre-dispute consent to jurisdiction over internet transactions. We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Comply with Website Privacy Policies Under California's Online Privacy Protection Act of 2003 (OPPA)
Privacy & Information Security, Types of Privacy Protections, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Review the requirements in California’s Online Privacy Protection Act of 2003 (CalOPPA) (Bus. & Prof. Code §§ 22575–22579) for website privacy policies. We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Chart: Types of Invasion of Privacy Claims
Privacy & Information Security, Types of Privacy Protections, Workplace Privacy, Financial Data Privacy, Health Information Privacy, Internet and Electronic Privacy, Information Security Planning, Handling Employee Data, Handling Health Information, Handling Internet and Electronic Data
Use this chart to become familiar with the different types of invasion of privacy claims. These include the traditional common law invasion of privacy torts of intrusion into private matters, public disclosure of private facts, publicity placing a person in a false light, and misappropriation of a person’s name or likeness.
-
Chart: Definitions under the California Consumer Privacy Act (CCPA)
Privacy & Information Security, Types of Privacy Protections, Financial Data Privacy, Internet and Electronic Privacy, Information Security Planning, Handling Internet and Electronic Data
Use this chart to become familiar with the definitions under the California Consumer Privacy Act of 2018 (CCPA) (Civ. Code, §§ 1798.100–1798.199.100) as amended by the California Privacy Rights Act of 2020 (CPRA). We completed legal editing and analysis of authorities cited here as of the date listed above.
-
Analyzing Unfair or Deceptive Business Practices Arising from Inadequate Data Security
Privacy & Information Security, Types of Privacy Protections, Information Security Planning, Handling Internet and Electronic Data
Review how a business’s failure to properly protect private data could be subject to unfair or deceptive business practices prosecution under federal and state law. We completed legal editing and analysis of authorities cited here as of the date listed above.
No programs found.
No secondary sources available.